AVAILABLE 24x7
888.662.2724
AVAILABLE 24x7
(888) 66CARAH
Fast & Accurate
Request A Quote

Quick Response
Chat With Us

ArmorxAI Datasheet
RansomObserver: See Before You Enforce. Deploy RansomObserver with Confidence.
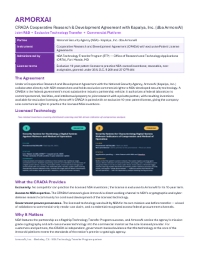
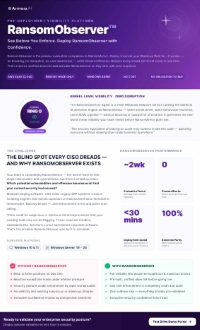
Discover how the RansomObserver Agent helps organizations evaluate ransomware threats before enabling active protection. Running the same AI detection engine, kernel driver, behavioral heuristics and AI/ML pipeline as RansomArmor, the Windows endpoint service provides real-world threat visibility without blocking or quarantining binaries.
Access the resource to learn how organizations can:
-
Assess ransomware activity before active enforcement
-
Gain visibility into real-world endpoint threats
-
Evaluate behavioral detection capabilities
-
Use the same detection engine as RansomArmor
-
Monitor threats without blocking or quarantine
-
Prepare for a smoother RansomArmor deployment

Download the Resource