
Why agencies choose RapidFort
The leader in software supply chain security
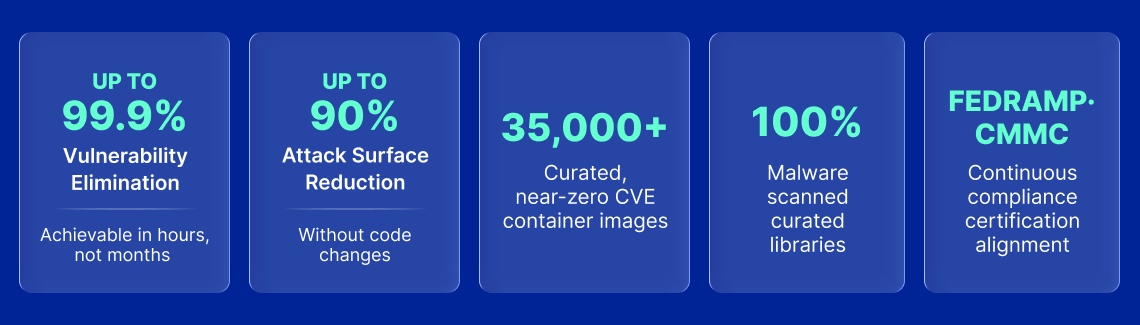
RapidFort is the leader in Software Supply Chain Security, enabling organizations to eliminate risk across their software stack at scale. As AI accelerates software development and the speed at which vulnerabilities are exploited, open-source risk has become a critical operational priority for public-sector organizations. Its platform combines curated near-zero CVE container images, runtime profiling, and attack surface management to remove up to 99.9% of vulnerabilities within hours and reduce the attack surface by up to 90% without code changes
Secure Foundation with Near-Zero CVE Images
Government agencies, defense organizations, and public sector entities require a verified, compliant starting point for every software environment on which their missions depend. RapidFort delivers FIPS 140-2- and 140-3-validated, STIG- and CIS-benchmarked container images across all major Linux distributions, establishing a near-zero CVE baseline before development begins
Continuous CVE Elimination Across the Software Lifecycle
Every containerized workload is profiled to identify what is actively used at runtime, generating a Software and Runtime Bill of Materials for complete supply chain visibility. Unused components are automatically removed, false positives eliminated, and images continuously hardened, reducing the software attack surface by up to 90%. This ensures ongoing compliance with FISMA, FedRAMP, and NIST 800-53 mandates without increasing engineering teams' remediation workload.
Federal Compliance Alignment
RapidFort aligns with the compliance frameworks that government agencies and public sector organizations operate under, maintaining that alignment continuously, not only at authorization time. Validated across FedRAMP, FISMA, NIST 800-53, and NIST 800-70, Zero Trust Architecture, CMMC, SOC2, PCI DSS, and HIPAA, the platform ensures every workload meets the security and compliance standards agencies are required to uphold.
Vendor-Agnostic, Highly Interoperable Security
RapidFort supports full operational flexibility across on-premises, cloud, and hybrid environments without vendor lock-in. Built on the open-source distributions that public sector teams already standardize on, including Red Hat, Ubuntu, Debian, and Alpine, RapidFort integrates with existing pipelines, container registries, and orchestration platforms without disrupting established infrastructure or workflows.
Curated Images
Start with a secure foundation. Near-zero CVEs from day one.
- 35,000+ near-zero CVE images, continuously patched and production-ready
- IPS 140-2 /3, STIG, CIS, NIST 800-70 hardened. Drop-in replacements.
- Ubuntu, Debian, Red Hat, Alpine. No vendor lock-in.
Curated Libraries
Most supply chain attacks enter through open-source dependencies. Stop them here.
- Malware-scanned packages for npm, PyPI, and more
- Pin-for-pin compatible, zero workflow changes required
- Covers the ecosystems most targeted in enterprise and AI workloads
RapidFort Analyzer
Cut through scanner noise. Know exactly which CVEs actually apply.
- Validates CVE applicability: not just what is installed, but what is real
- Exploit-aware Rapid Risk Score for focused, actionable prioritization
- SBOM export in SPDX, CycloneDX, JSON, and CSV
RapidFort Optimizer
Remove every component your application never uses.
- Up to 99.9% CVE elimination from unused code paths
- Up to 90% attack surface reduction via RBOM®-validated hardening
- Hardened images automatically rebuilt every 24 hours, drop-in ready
RapidFort Profiler
Your scanner sees what is installed. Profiler sees what actually runs.
- Generates RBOM®, RapidFort's proprietary Runtime Bill of Materials
- Separates real exploitable risk from theoretical CVE noise
- Under 1% overhead. No code changes. No disruption
RapidFort CART
Compliance that stays current, not a point-in-time audit.
- US : FedRAMP, CMMC, cATO, DISA STIG, FIPS, NIST 800-53, NIST 800-190, SOC 2, PCI DSS
- EU: NIS 2, CRA, SLSA. Validated via the OpenSCAP framework.
- Drift detected immediately. Audit ready reports and remediation scripts auto-generated.
Supporting the 2026 President's Cyber Strategy for America
RapidFort is directly aligned with three core pillars of the 2026 President's Cyber Strategy for America: modernizing and securing federal networks, securing critical infrastructure across all 16 CISA sectors, and sustaining U.S. superiority in critical and emerging technologies. Through one-for-one image swaps without recoding, downtime, or loss of functionality, RapidFort enables agencies to accelerate modernization without operational disruption.
End-to-End Security Without Compromise
With RapidFort, government agencies, defense organizations, and public sector entities build, deploy, and maintain continuously hardened workloads across the full software supply chain, with no gaps, no handoffs, and no blind spots. RapidFort enables organizations to advance mission objectives, continuously reduce risk, and protect the national and citizen data that their missions are built to serve